Information Security Governance & Policies
91%Experienced in developing and reviewing IT and information security policies and procedures in alignment with PCI, GDPR and ISO standards, supporting organizations in strengthening their information security governance frameworks.
Regulatory & Payment Card Security
90%Experience assessing payment card security and regulatory compliance across banking environments, including SBP requirements, identifying control gaps and developing actionable recommendations to strengthen security and regulatory alignment.
Biography
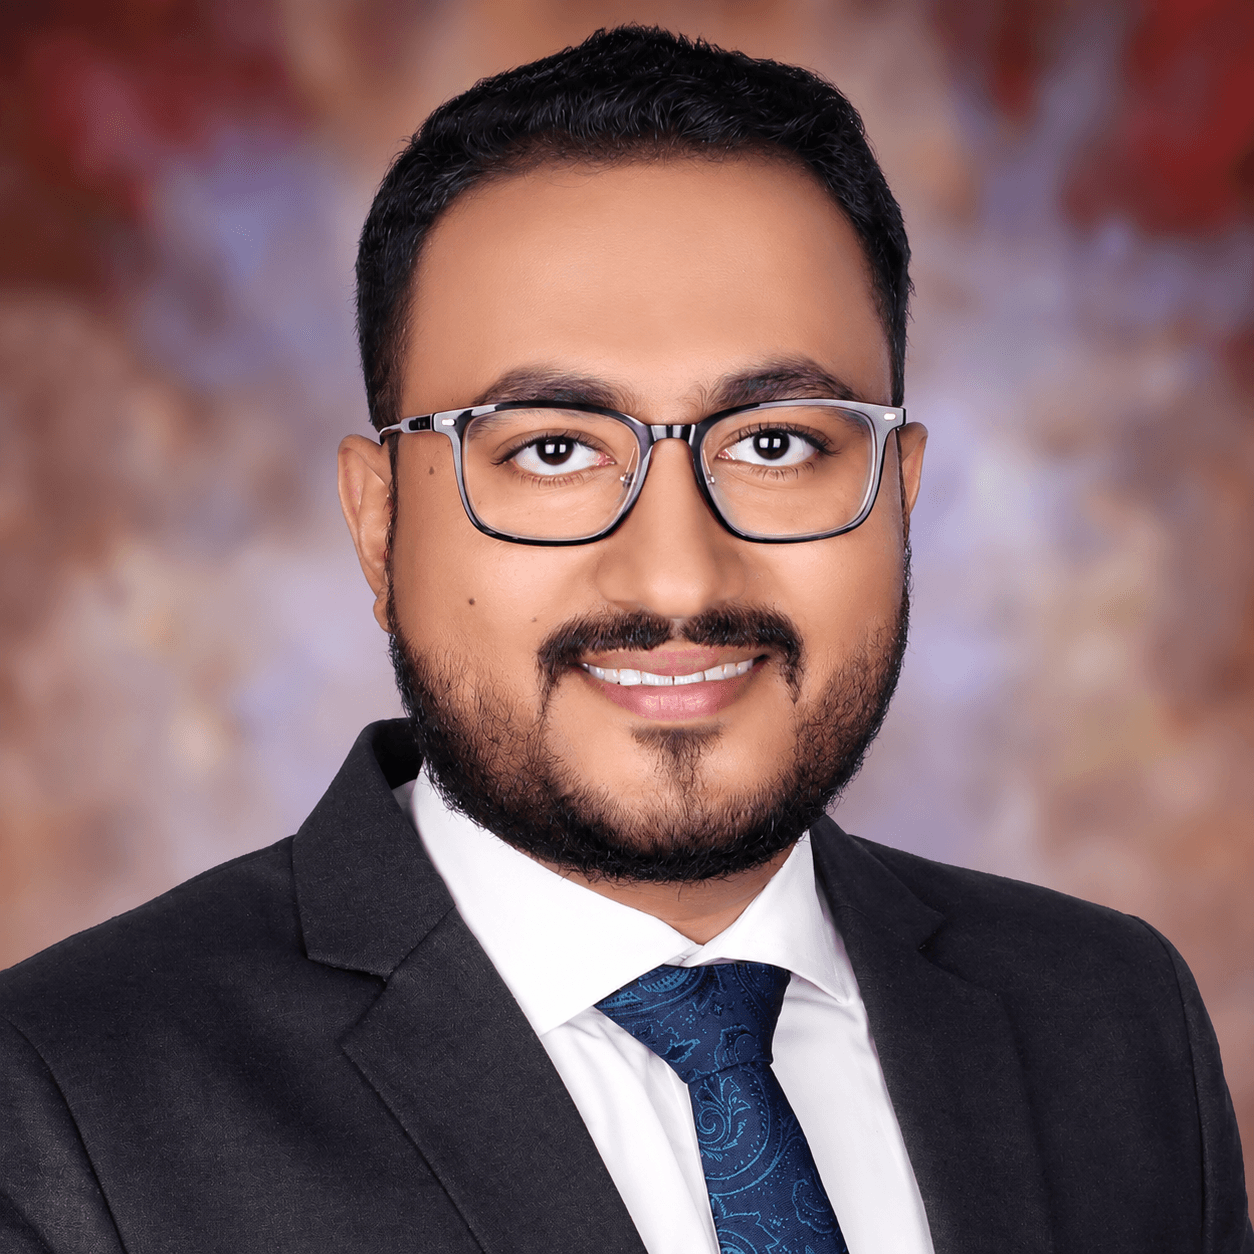
Usmanullah Khan is a Technology Risk and cybersecurity professional with over 3 years of experience in cybersecurity, business continuity planning, IT risk management and technology assurance. He has experience supporting organizations in strengthening information security controls, protecting critical IT infrastructure and improving resilience across regulated and technology-driven environments.
As Senior Consultant – Cybersecurity & Risk Advisory at Infinitrs, he leads a team of professionals and supports engagements covering cybersecurity risk management, ITGC, business continuity, IT audits and regulatory compliance. His experience includes cybersecurity risk assessments, third-party risk management, payment card security assessments, BCDRP, ITGC testing and information security policy development. He has also gained professional exposure at KPMG and worked with regulatory and international standards including NCA, SBP, ISO 22301, ISO 27001/27002, PCI and GDPR. His multidisciplinary expertise enables organizations to strengthen technology controls, manage cyber risks and enhance information security and operational resilience.
Professional skills
Cybersecurity Risk Management
94%Experienced in developing cybersecurity risk management frameworks, conducting application risk assessments and implementing third-party risk management strategies to identify and mitigate technology and security risks.
ITGC & Technology Assurance
93%Strong experience in IT General Controls testing, information security assessments, incident management reviews and evaluation of technology controls against regulatory requirements and organizational policies.
Business Continuity & Disaster Recovery
92%Experienced in Business Continuity and Disaster Recovery Planning, including BIA, RPO, RTO and MTD assessments, with a focus on aligning resilience strategies with ISO 22301 and ISO 22317 requirements.
Request a quote for work
Feel free to contact us through Twitter or Facebook if you prefer!